Why DMARC?
Because DMARC Turns Security Into Strategic Value
DMARC improves your email deliverability, and helps keep your messages out of the spam folder.
Better yet, DMARC shows you who’s sending email on your behalf and lets you block fraudsters.
On top of that, Gmail, Yahoo and Outlook.com now require DMARC from bulk senders, so it is no longer optional for most brands.
The Visibility Advantage Only DMARC Offers
Clear Insight Into Your Domain's Email Ecosystem
While SPF and DKIM handle basic email authentication, DMARC takes it a step further.
Every DMARC record includes a field where you can specify an email address to receive detailed feedback from inbox providers.
Whenever an email claiming to be from your domain is received, participating mail servers generate a report summarizing the outcome:
These measures aim to protect users from phishing and spoofing attacks by ensuring that only authenticated emails reach recipients' inboxes. Non-compliant senders risk having their emails filtered or rejected.
Enforcing DMARC is one of the most common ways to meet requirement 5.4.1 and protect customers from spoofed email.
Financial Services & Fintech
Banks, credit unions, neobanks, payment processors, digital wallets, and fintech platforms that handle cardholder data.
Retail & eCommerce
Online stores, brick-and-mortar retailers, and point-of-sale vendors who accept credit card payments.
Healthcare
Hospitals, clinics, and healthcare SaaS providers that process payments for services or store billing data.
Travel & Hospitality
Airlines, hotels, car rental companies, and booking platforms that process online payments.
Education
Universities and educational institutions collecting tuition or fees via credit/debit cards.
Billing & Subscription Services
SaaS providers, utility companies, streaming services, and platforms with recurring payment models.
Professional Services
Legal firms, consulting agencies, and accountants that bill clients via card payments.
Every DMARC record includes a field where you can specify an email address to receive detailed feedback from inbox providers.
Whenever an email claiming to be from your domain is received, participating mail servers generate a report summarizing the outcome:
- Did it pass SPF?
- Did it pass DKIM?
- Was it DMARC aligned?
DMARC In Action: Tangible Business Benefits
- Improved email engagement rates
Legitimate emails land more reliably in the inbox, boosting open rates and click-throughs.
- Improved email deliverability
DMARC reporting makes it easy to spot misconfigured senders and fix issues before they affect your campaigns.
- Reduced risk of domain blacklisting
By blocking unauthorized senders, DMARC helps maintain a clean domain reputation across email platforms.
- Streamlined third-party email management
DMARC visibility lets you audit every platform sending on your behalf—marketing tools, CRMs, billing systems, and more.
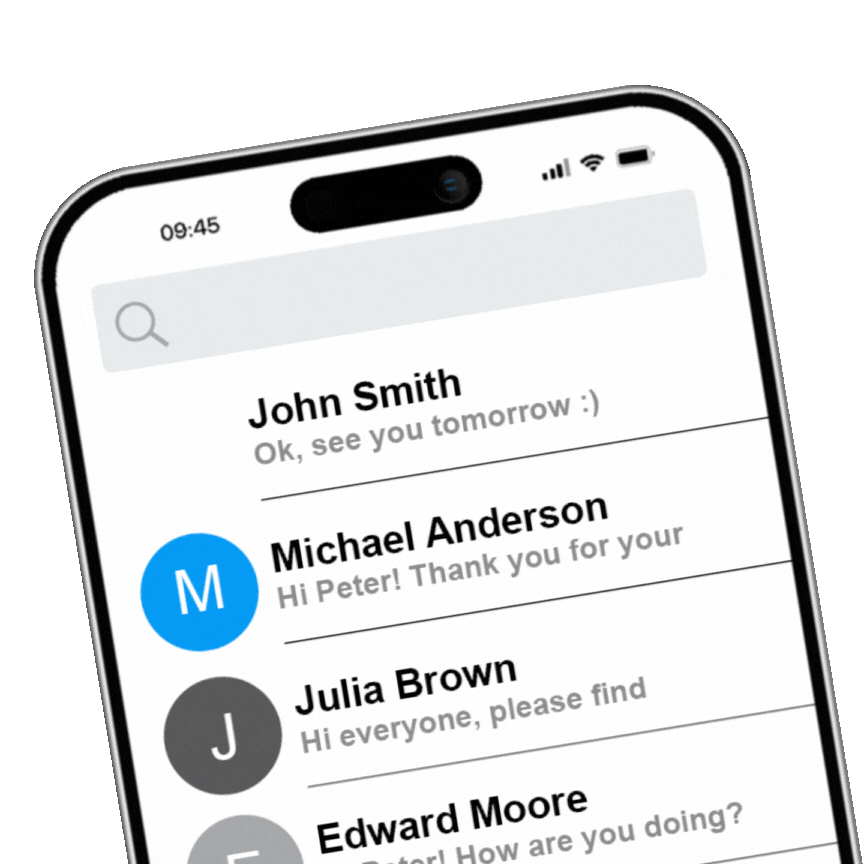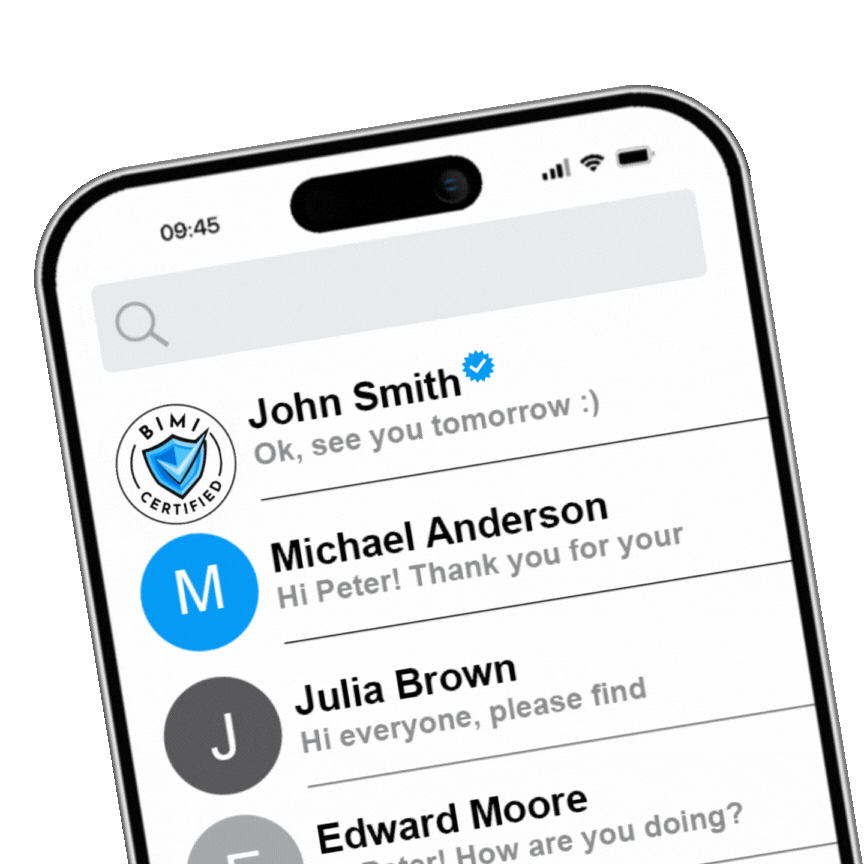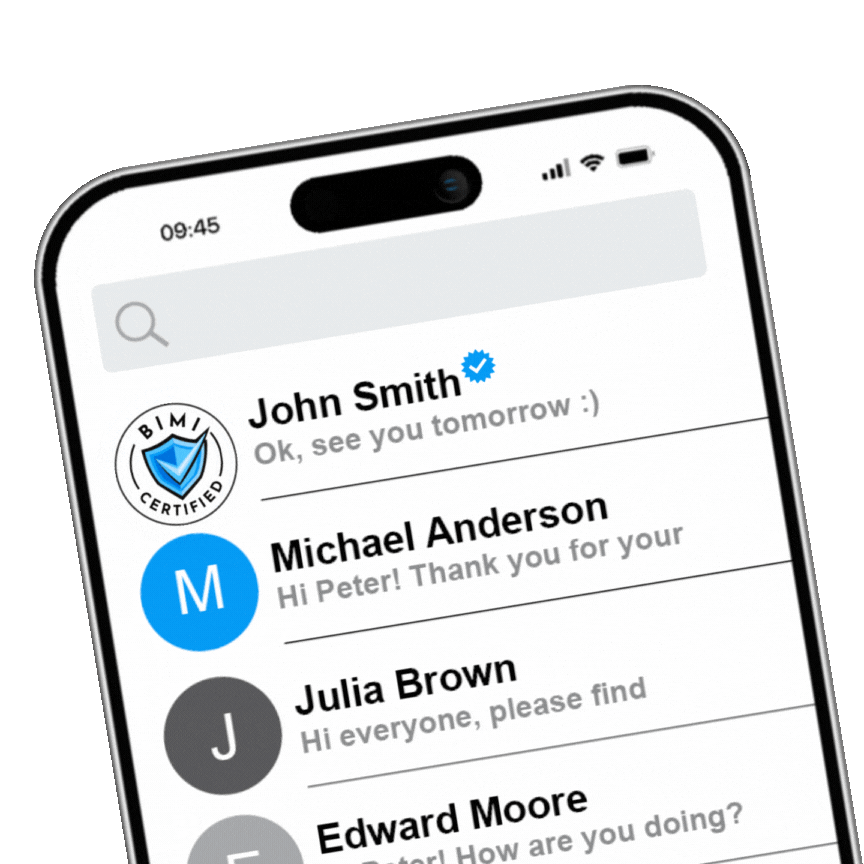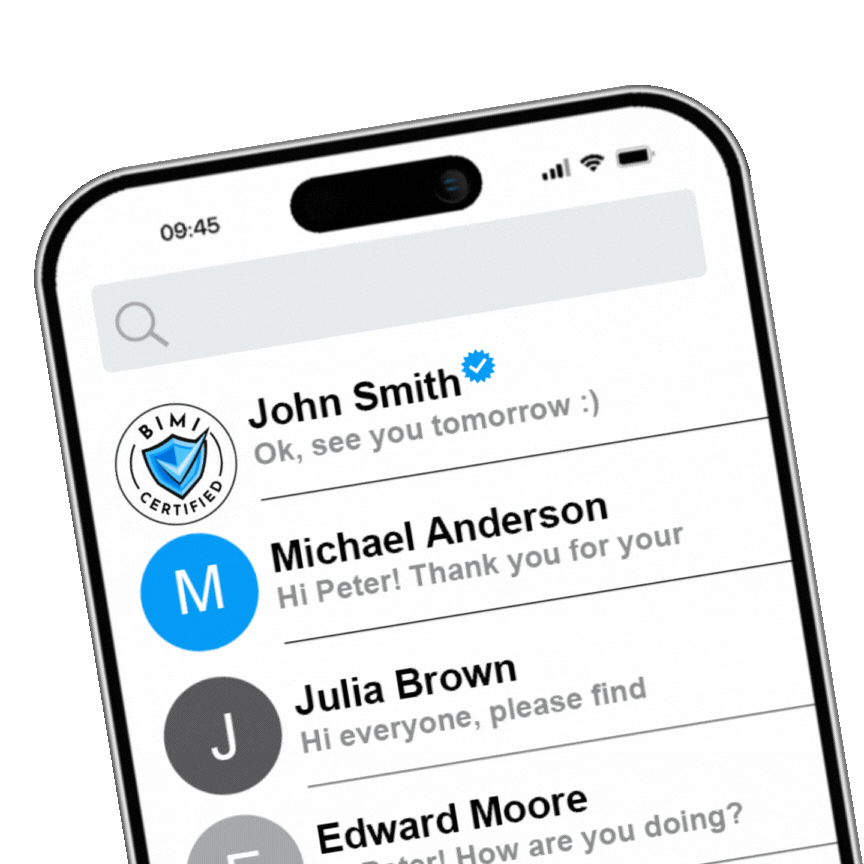
- Foundation for BIMI and VMC certification
Once DMARC is enforced, your brand is eligible to display a verified logo in supported inboxes—boosting recognition and trust instantly.
The Ever Growing Adoption of DMARC
The U.S. government made DMARC mandatory for federal agencies in 2017 (CISA Binding Operational Directive 18-01)—and since then, organizations and governments worldwide have followed suit.Microsoft Outlook’s New Rules on DMARC
Since May 5, 2025, Outlook.com has required domains that send more than 5,000 emails a day to its users to pass SPF and DKIM and publish a DMARC policy.These measures aim to protect users from phishing and spoofing attacks by ensuring that only authenticated emails reach recipients' inboxes. Non-compliant senders risk having their emails filtered or rejected.
PCI DSS 4.0.1 Requires Anti-Phishing Controls
Since March 31, 2025, PCI DSS 4.0.1 (requirement 5.4.1) has required organizations that handle card data to have automated mechanisms that detect and protect people against phishing.Enforcing DMARC is one of the most common ways to meet requirement 5.4.1 and protect customers from spoofed email.
Financial Services & Fintech
Banks, credit unions, neobanks, payment processors, digital wallets, and fintech platforms that handle cardholder data.
Retail & eCommerce
Online stores, brick-and-mortar retailers, and point-of-sale vendors who accept credit card payments.
Healthcare
Hospitals, clinics, and healthcare SaaS providers that process payments for services or store billing data.
Travel & Hospitality
Airlines, hotels, car rental companies, and booking platforms that process online payments.
Education
Universities and educational institutions collecting tuition or fees via credit/debit cards.
Billing & Subscription Services
SaaS providers, utility companies, streaming services, and platforms with recurring payment models.
Professional Services
Legal firms, consulting agencies, and accountants that bill clients via card payments.
If You’re Late to the DMARC Party, We’ve Got You Covered
Join the growing list of organizations protecting their domains, improving deliverability, and preparing for BIMI.
Now’s the time to adopt DMARC with confidence.
Get the security right, and the brand visibility follows.